Walk Into Your Audit With the Evidence Ready
For companies preparing for ISO 27001, a customer's security review, or an internal or statutory IT audit.
We find the gaps against ISO/IEC 27001:2022 and your key control objectives, help you fix them, and build the evidence packs, so the auditor sees controls that actually work instead of a last-minute scramble.
Free 30-minute call. No obligation.
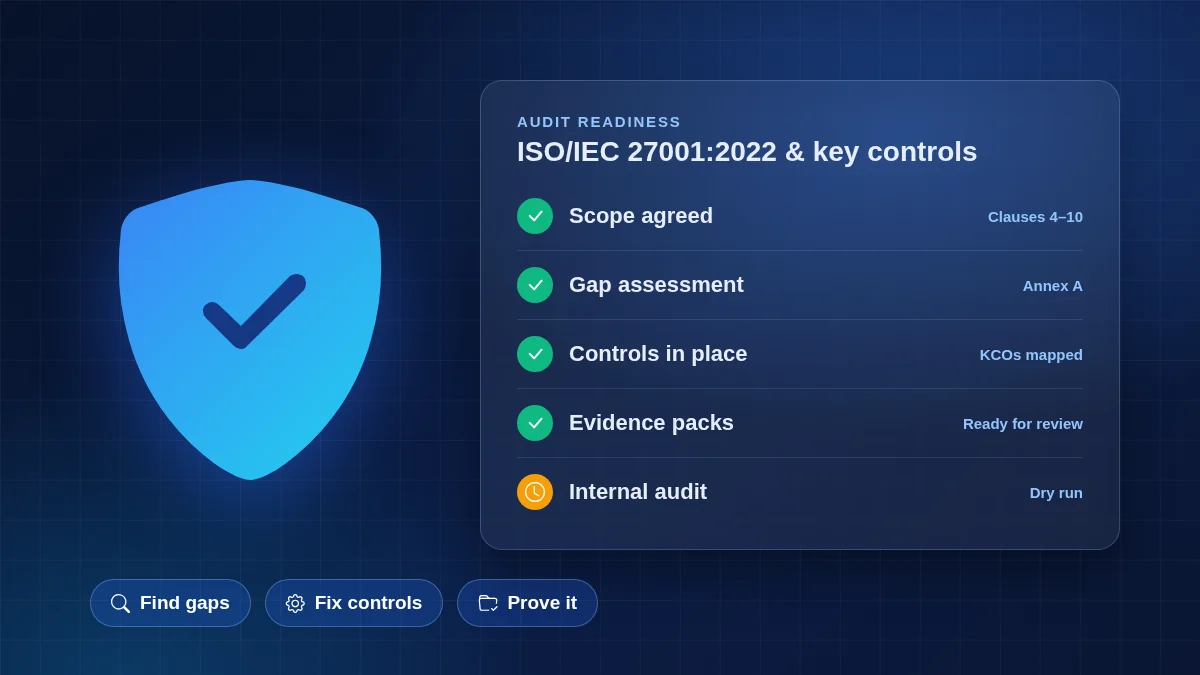
What audit readiness gives you
Audits rarely fail because a company has no controls. They fail because controls are not written down, not followed consistently, or cannot be proven. We fix all three.
Know your gaps early
A structured review against ISO 27001 and your key control objectives shows exactly what is missing, ranked by risk and effort, months before the auditor arrives.
Controls that actually run
Access reviews, change approvals, backups and incident handling set up as simple routines your team follows, not policies that sit in a folder.
Evidence ready before they ask
For every control, an evidence pack showing what was done, when and by whom, so audit fieldwork is quicker and findings are fewer.
How we get you ready
-
01
Scope
We agree which locations, systems, teams and standards the audit will cover.
-
02
Assess gaps
We review policies, processes and systems against the requirements and list the gaps.
-
03
Fix & document
We help put controls in place and build the documents and evidence auditors expect.
-
04
Dry run
We run an internal audit, close the findings, and prepare your team for audit day.
Ways to work with us
These are starting points. Most clients start with a gap assessment, which gives you a clear list of what to fix and a realistic timeline.
ISO 27001 Gap Assessment
For companies starting ISO 27001 or checking where they stand
Fixed quote after your free call
- Scope definition for your management system
- Review against ISO/IEC 27001:2022 clauses and Annex A
- Gap report ranked by risk and effort
- Roadmap and timeline to certification audit
ISO 27001 Implementation Support
For companies working towards certification
Fixed quote after your free call
- Everything in ISO 27001 Gap Assessment
- Risk assessment and treatment plan
- Statement of Applicability
- Core policies and procedures
- Staff awareness session
- Internal audit and management review before the certification audit
IT Audit & Key Controls Readiness
For internal, statutory or customer IT audits
Fixed quote after your free call
- Mapping of key control objectives (KCOs) and IT general controls
- Walkthroughs of access, change, backup and operations controls
- Control testing and evidence packs
- Tracking and closure of audit findings
ISO 27001 certificates are issued by accredited certification bodies. We prepare you for the certification audit; we do not certify.
An IT services company asked for ISO 27001 by a key customer
A typical project for a growing company whose largest customer made ISO 27001 a condition of renewing the contract.
Before
- Security practices existed, but were not written down
- No risk register, and access to systems never reviewed
- Customer security questionnaires took weeks to answer
After
- A documented management system scoped to the business
- Quarterly access reviews and a live risk register
- Evidence packs ready for the certification audit and customer reviews
This is an illustration of a typical project, not a named client. Real case studies will be added here as they are published.
ISO 27001 and IT audit questions, answered
Book a Free Audit Readiness Call
Tell us what is coming up: ISO 27001, a customer questionnaire or an IT audit. We will talk through where you likely stand and what to prepare first.
- A first view of your likely gaps
- What auditors usually ask for, and in what form
- A realistic timeline to audit readiness
- Next steps, with a fixed quote for a gap assessment
Prefer to chat? Message us on WhatsApp
Tell us about your audit
Tell us about your business goals and we'll recommend the right AI, software, or automation solution.